Audit-proof
Complete traceability of your answers and results — audit-ready.
SCMC stands for Swiss quality in information security. Our ISMS platform combines simplicity, efficiency, and maximum security – replacing scattered Excel sheets with one central, online solution. All data is stored exclusively in a cloud environment operated in Switzerland – for maximum data security and full control.
With flexible assessment tools – from a quick Basic Cybersecurity Check to NIST-based standards and ISO/IEC 27001:2022 – companies of all sizes get the right solution to analyse, assess, and continuously improve their overall security level. No more Excel – manage information security easily online.
ISG reporting obligation in force since April 2025 — are you prepared?
New Self-learning module with HWZ
An ordinary Tuesday morning, and suddenly every system in your company stops. Do you know, as management, what to do now?
In about 50 minutes the self-learning module shows why information security is a leadership task, which questions you should ask and how to protect your company's most important assets. You learn to make the maturity of your information security visible and manageable, hands-on and without technical jargon. It was created with Heinz Stieger and the HWZ University of Applied Sciences in Business Administration Zurich for the CAS General Management. The module is in German.
The module is in German, runs on the Articulate learning platform and opens in a new window.
«SCMC Cyber-Risiken: Führung gefordert»
Every assessment follows the question catalogue of a module, such as the Swiss ICT minimum standard, ISO 27001, NIS2 or data protection. For each question you record the current state and the target, with a remark and a link to the evidence. The team works together in the project, every change stays in the history of the question, and for the next year you duplicate the assessment and carry on from there.
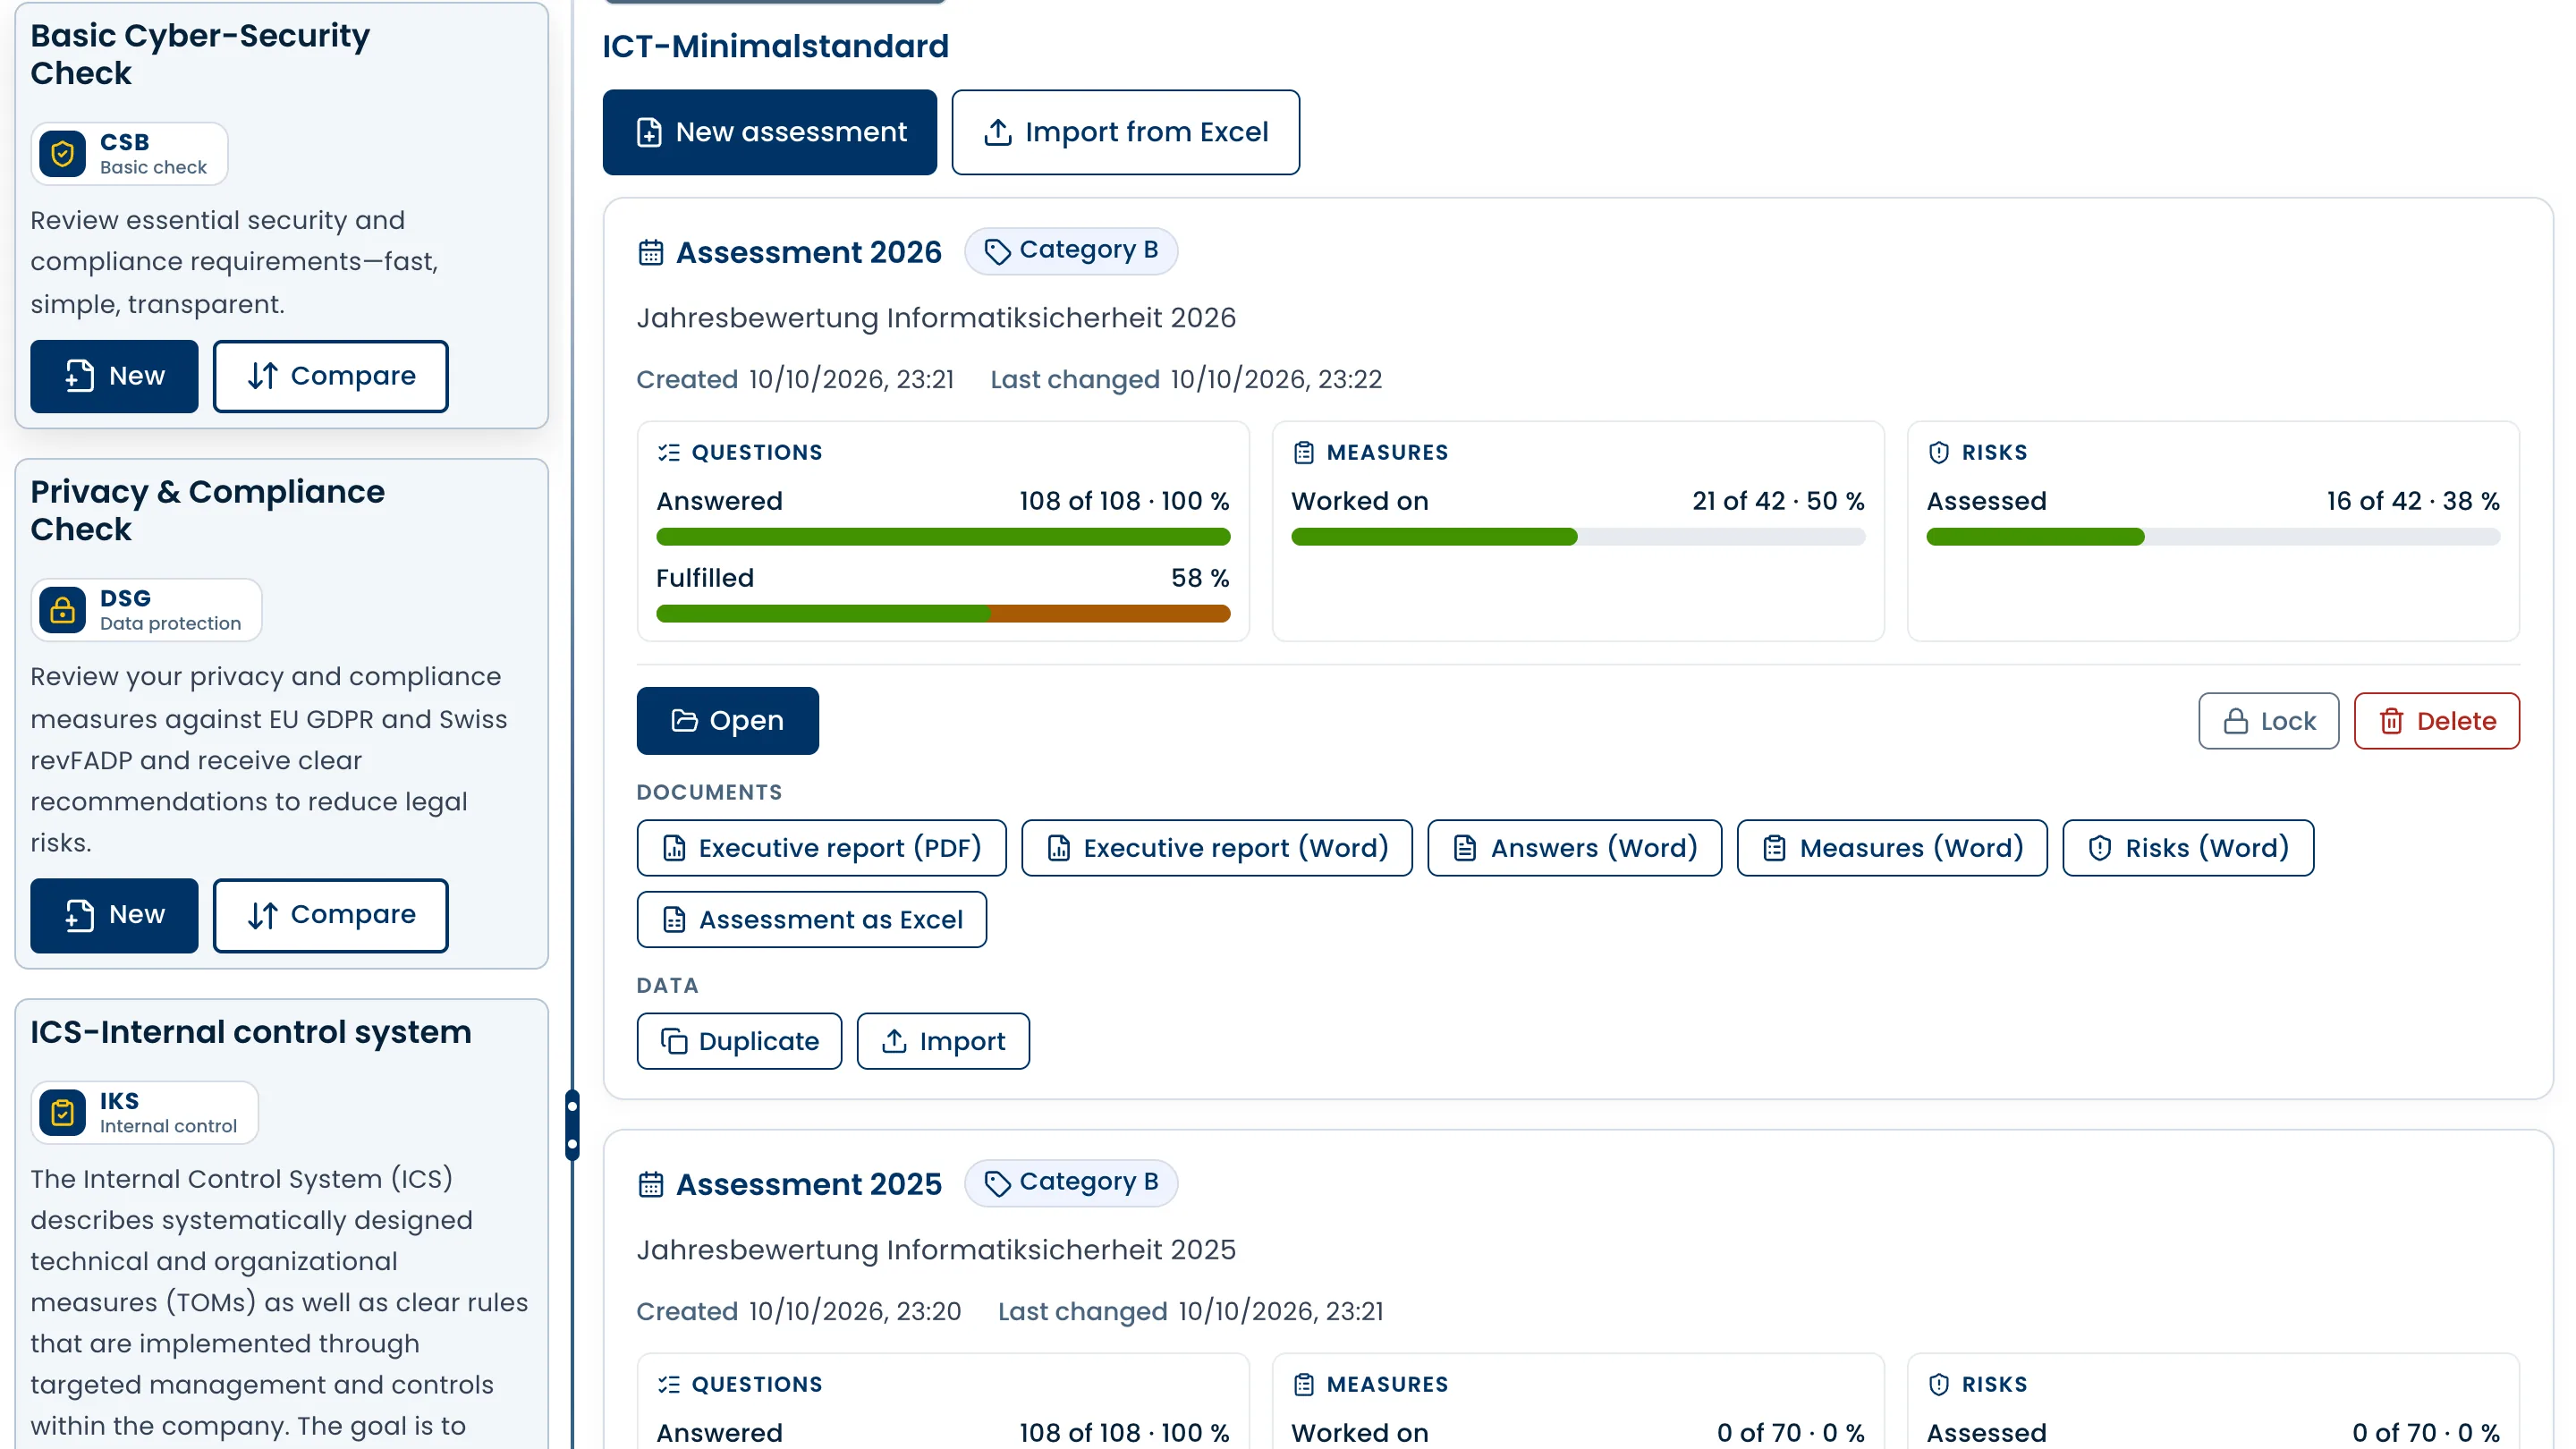
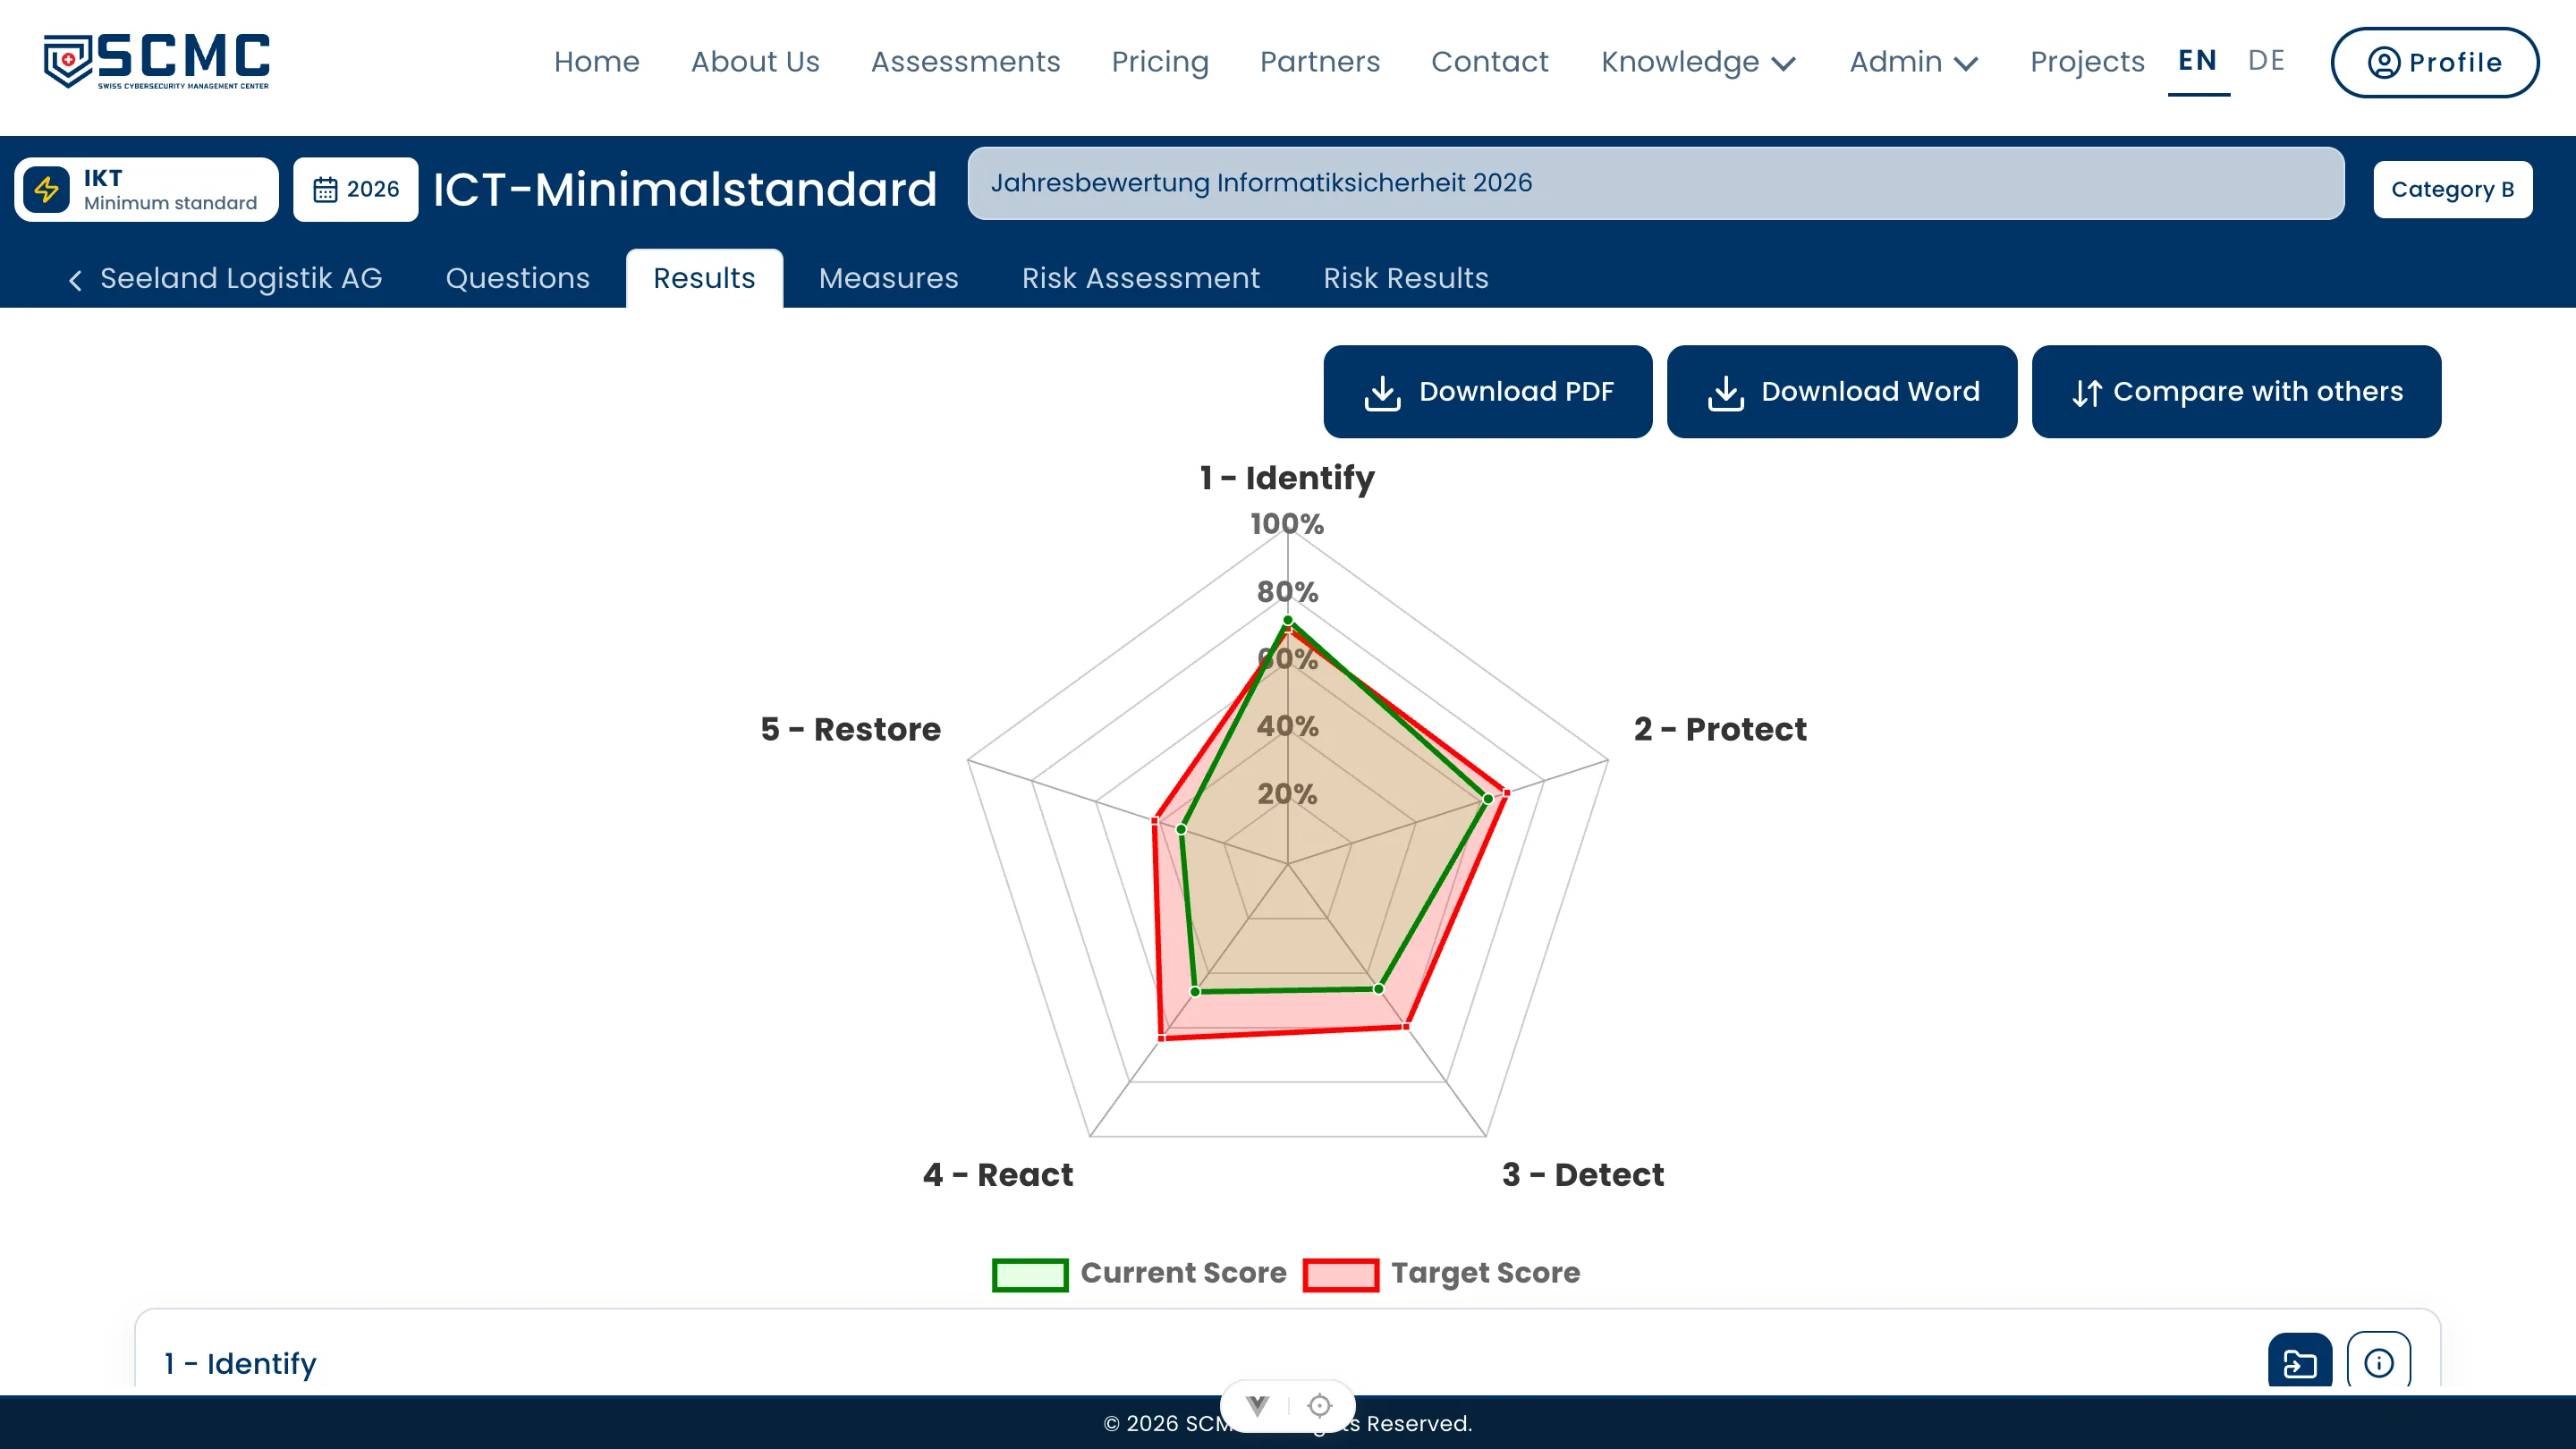
The results show current state and target per main area and area, as a radar chart and as a table with the gap in percentage points. Two years side by side show what has moved. For the management there is the report with a one-page summary as PDF or Word, and the executive report brings assessment, measures and risks together in one document.
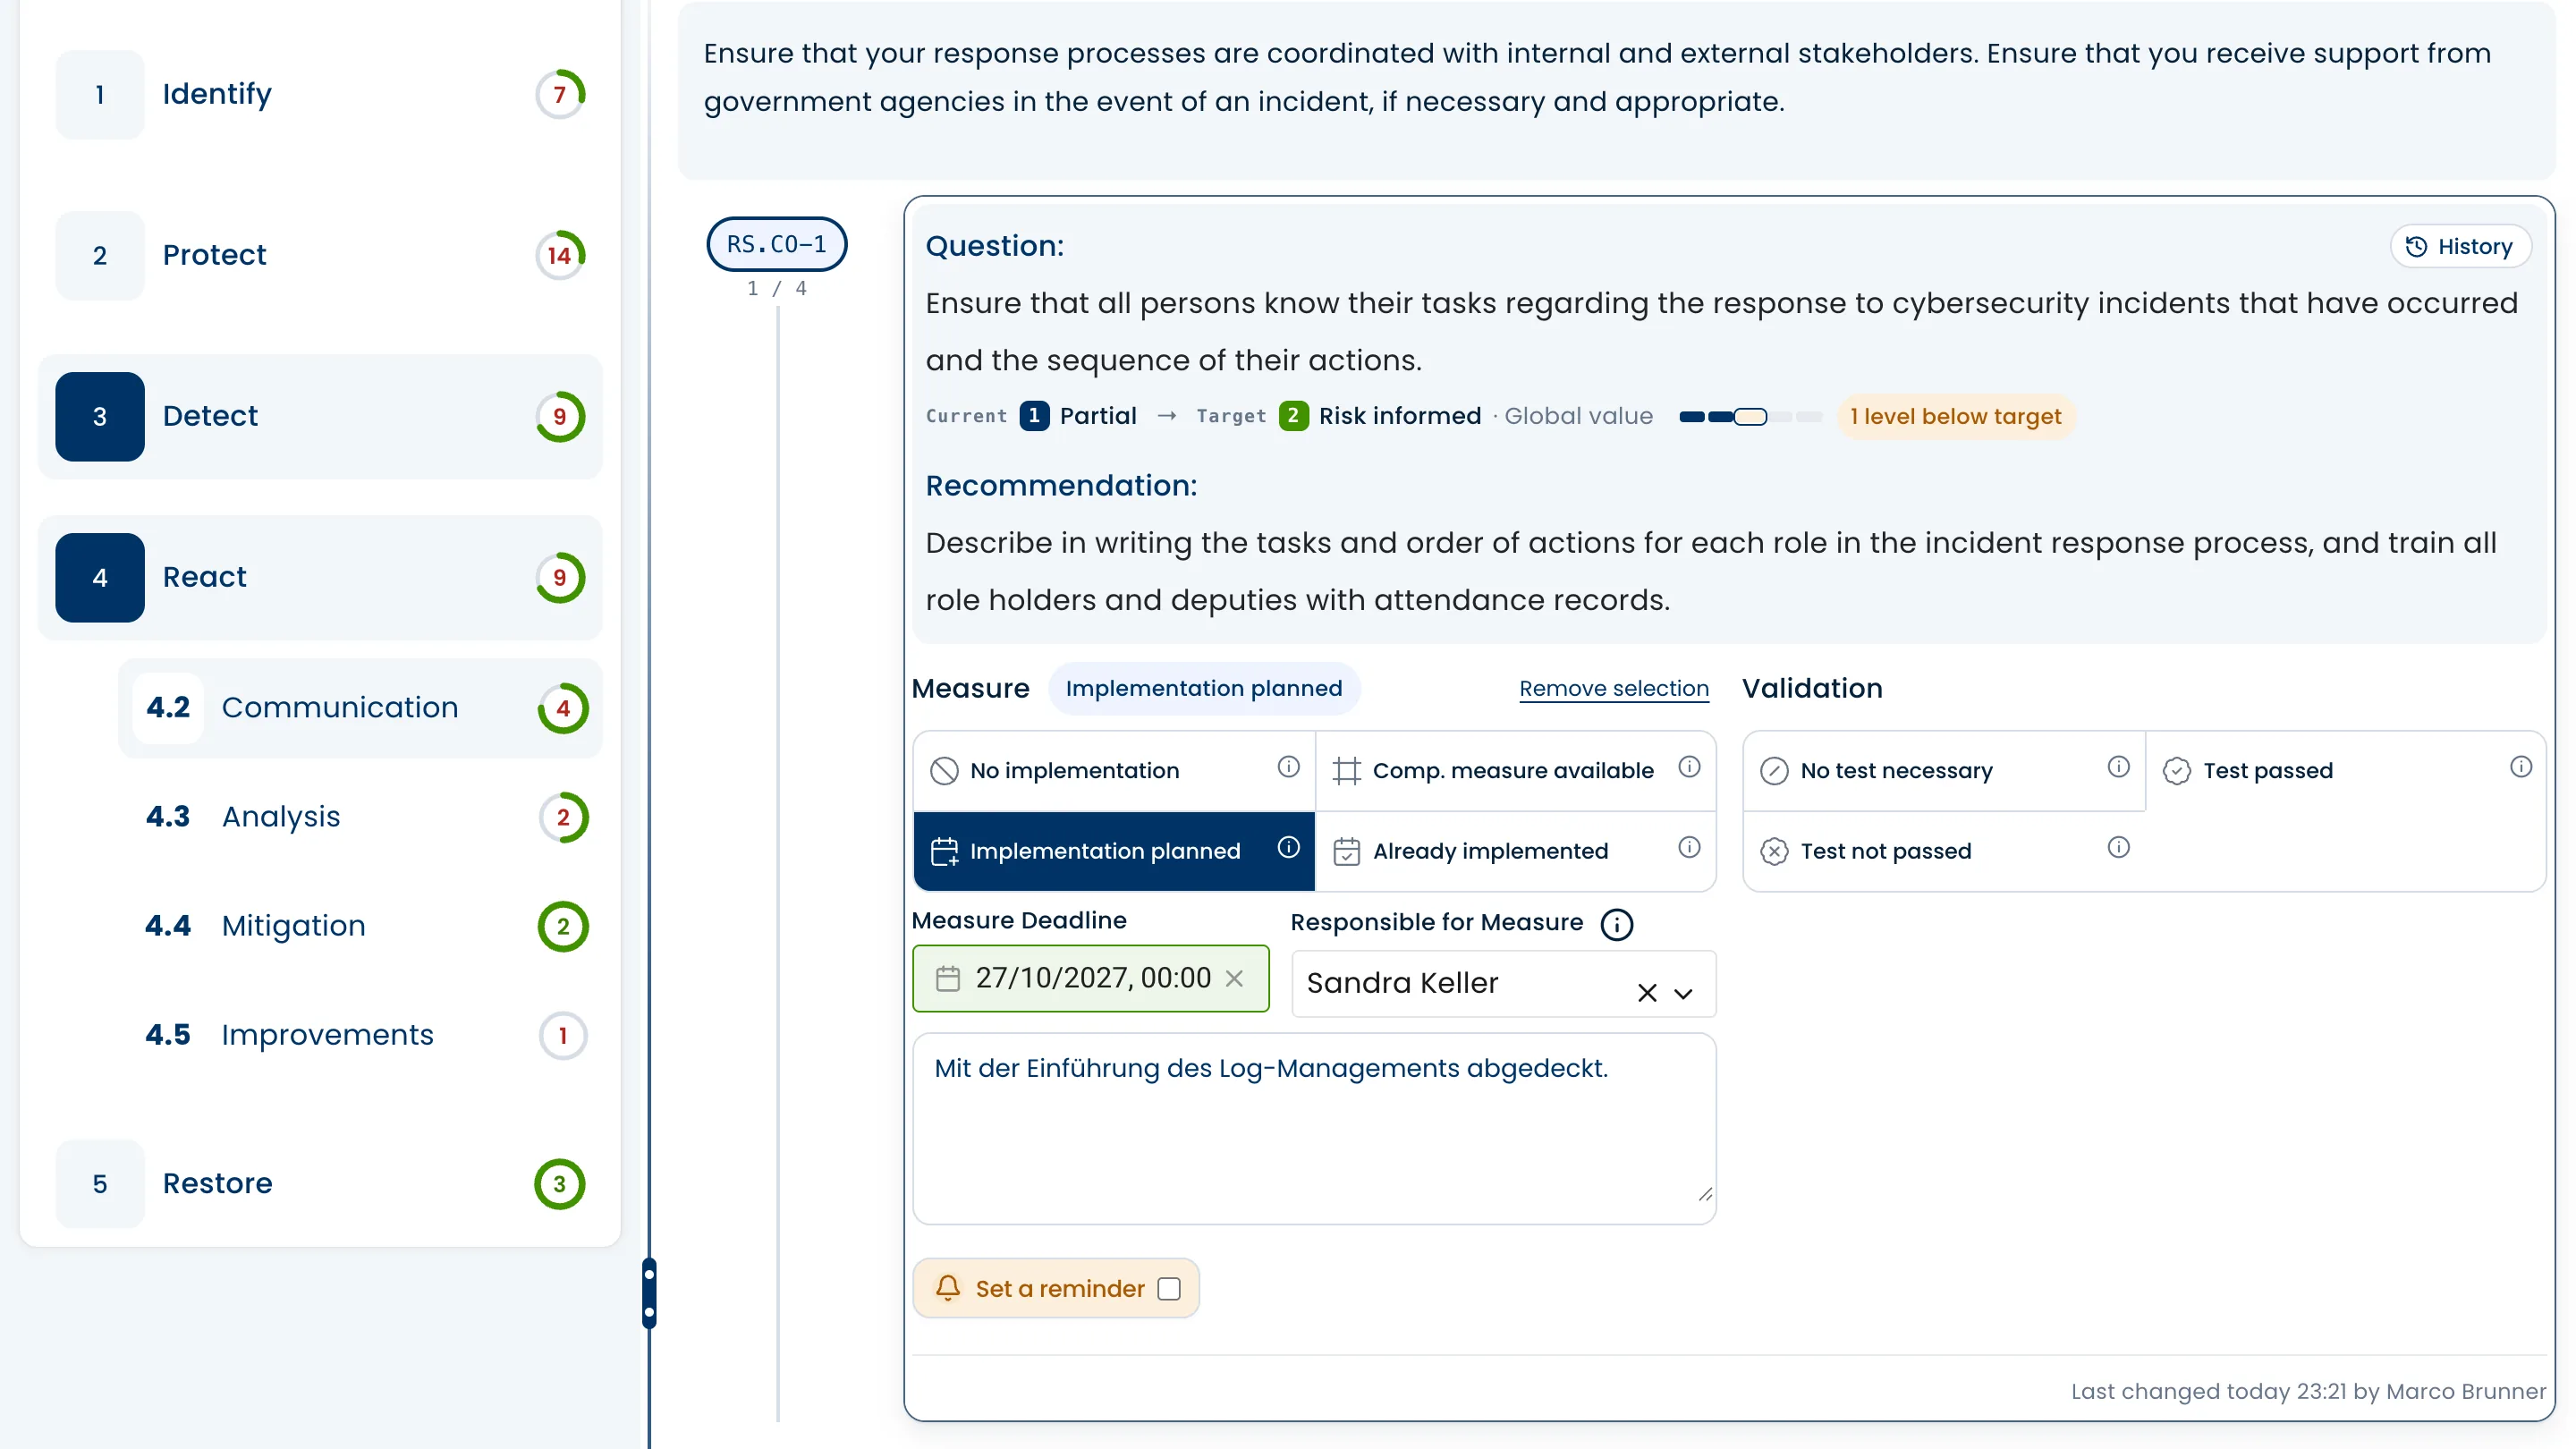
Every question below its target appears among the measures, with the recommendation of the module where it has one. You record what will be implemented, who is responsible, by when, and who checks the result. Overdue deadlines are marked, reminders go out by mail, and under "My Tasks" everyone sees what is on their desk.
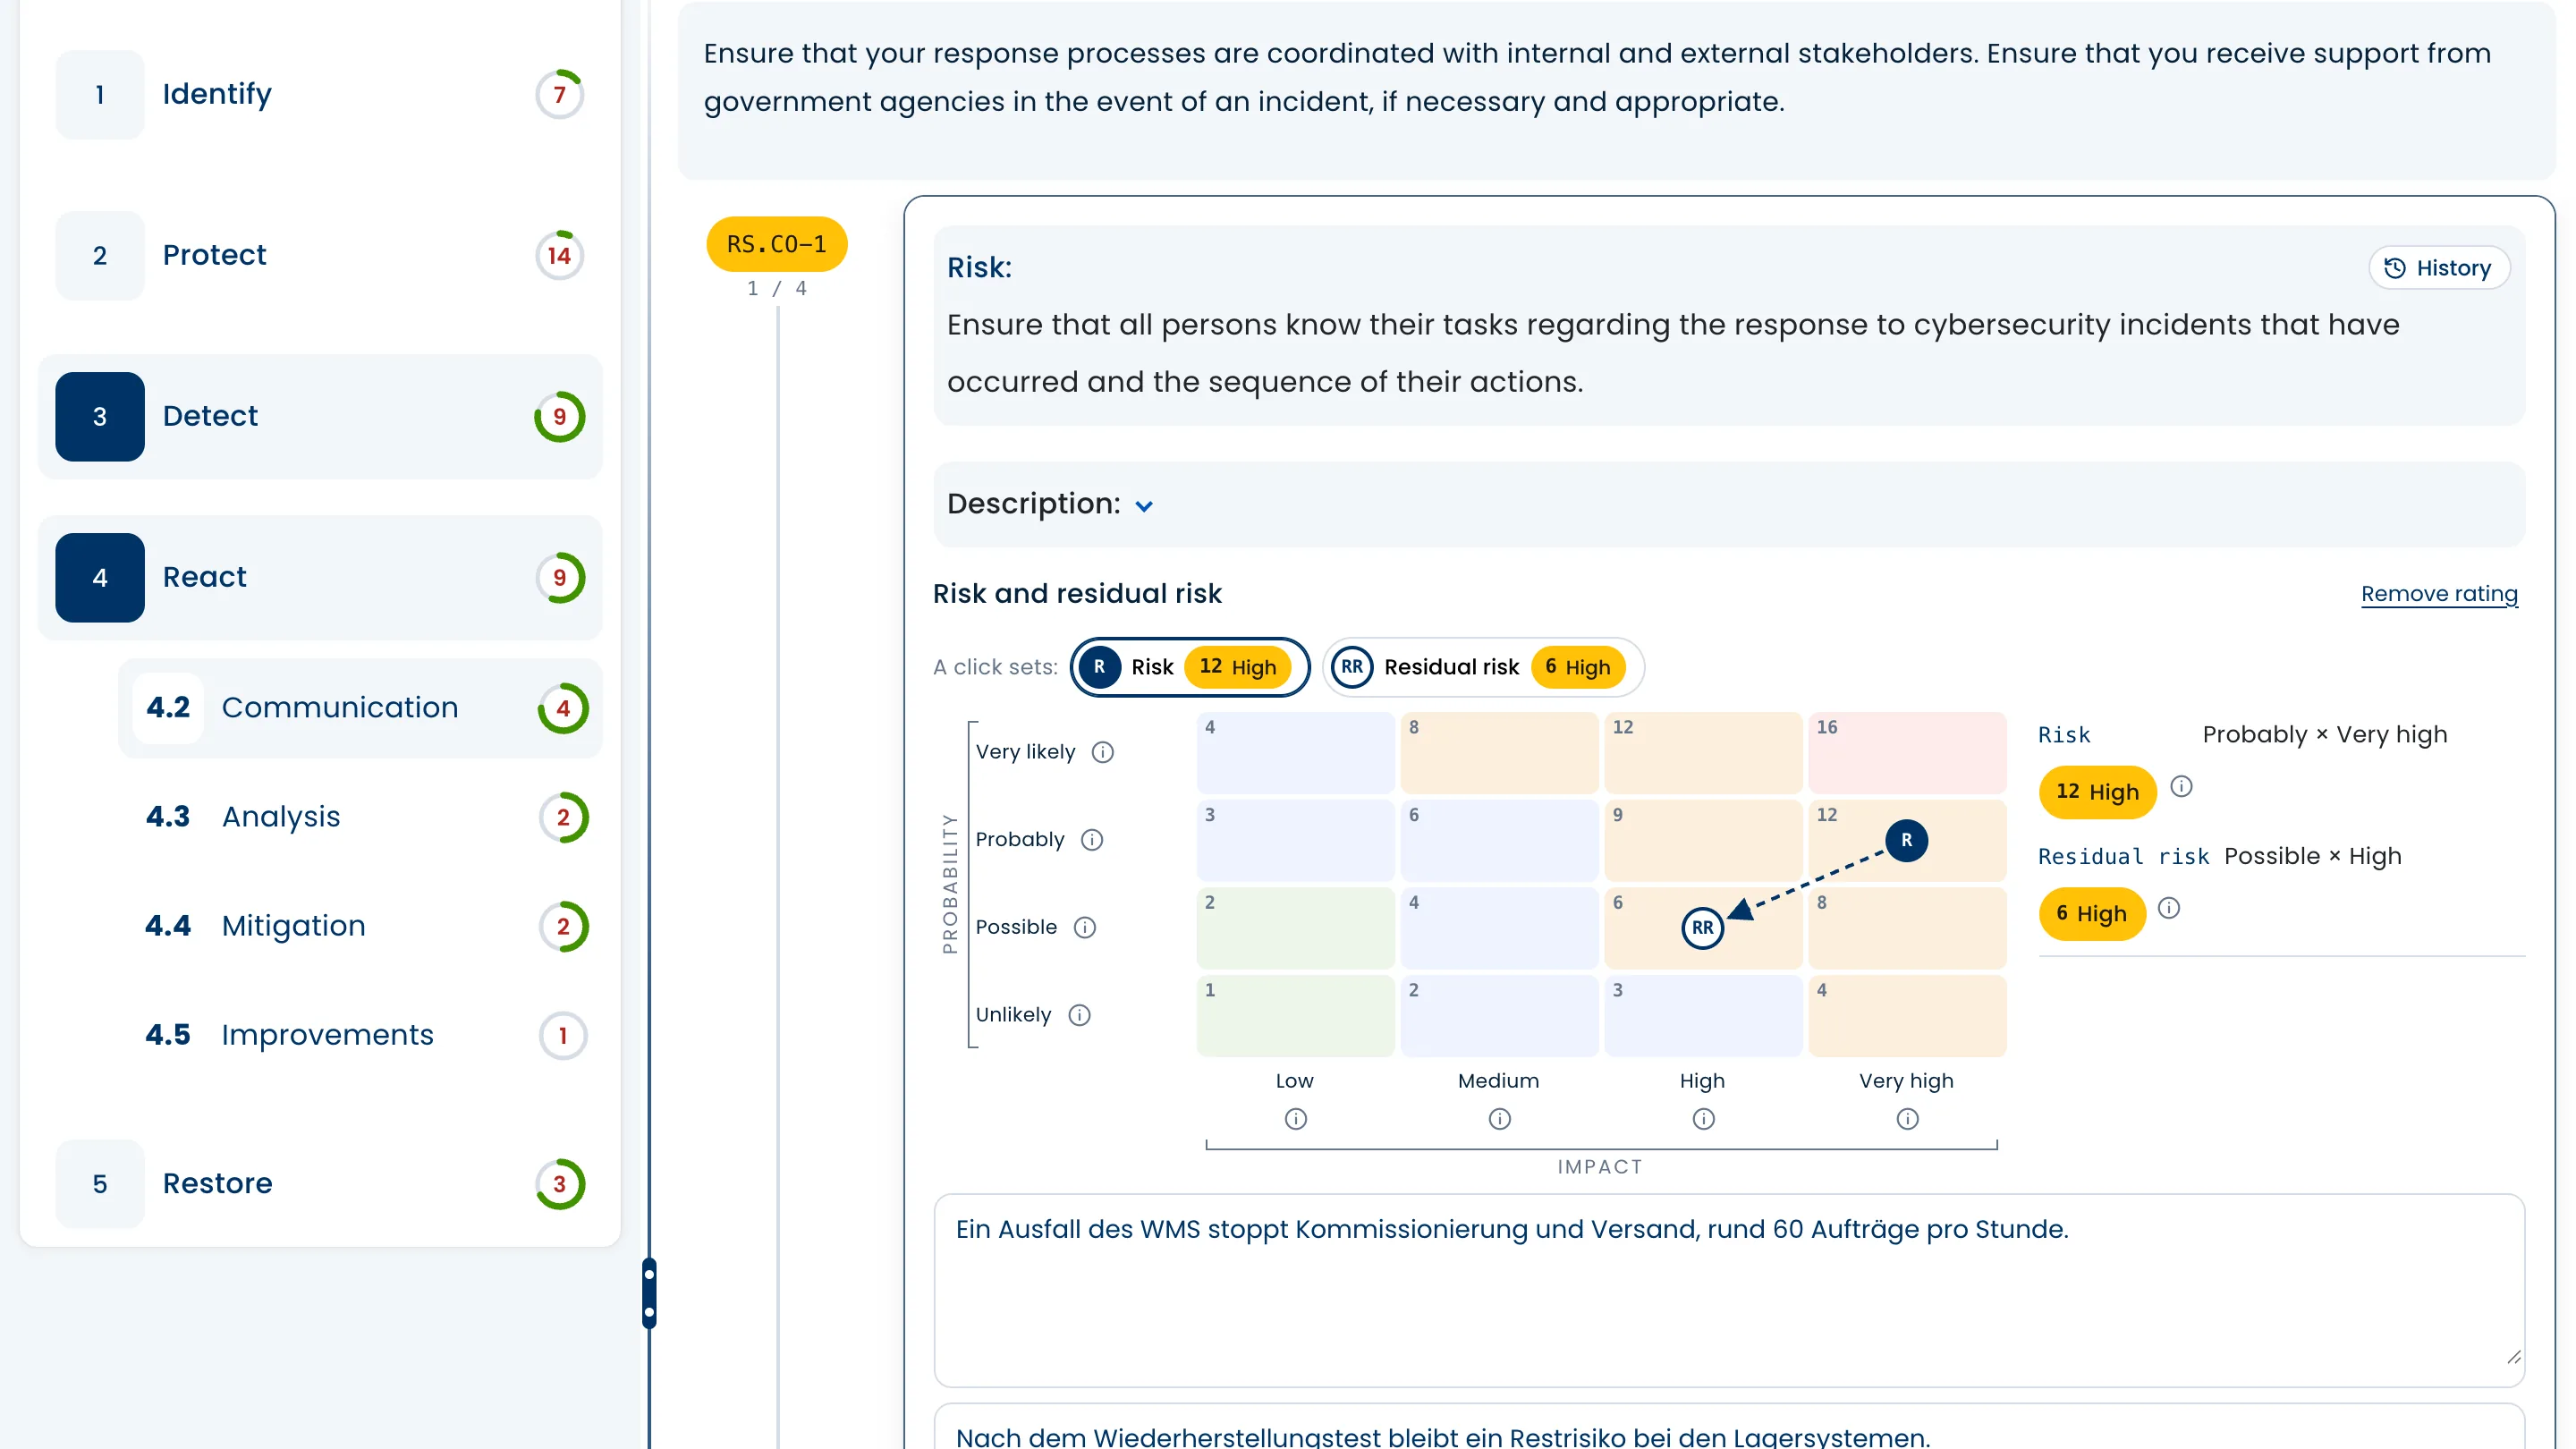
Where an answer is below its target, you rate the risk by probability and impact, right in the matrix. The residual risk after the measures follows, with its reasoning and evidence. The risk results show on one page how many positions are high, how the measures move them down the levels, and where no residual risk has been rated yet.
Simple, fast, transparent — three steps to a security assessment.
01
ISMS, ICT minimum standard, or individual framework.
02
Assign roles, assign sub-areas, see progress live.
03
Gap analysis, roadmap, management summary & audit export.
Compliance Made Simple. Security Made Strong. Confidence Made Possible.
Align with globally recognized cybersecurity and compliance frameworks.