Free and without subscription
All you need is an account. Zero Trust Maturity stays free, like the Basic Check.
Free · for SMEs
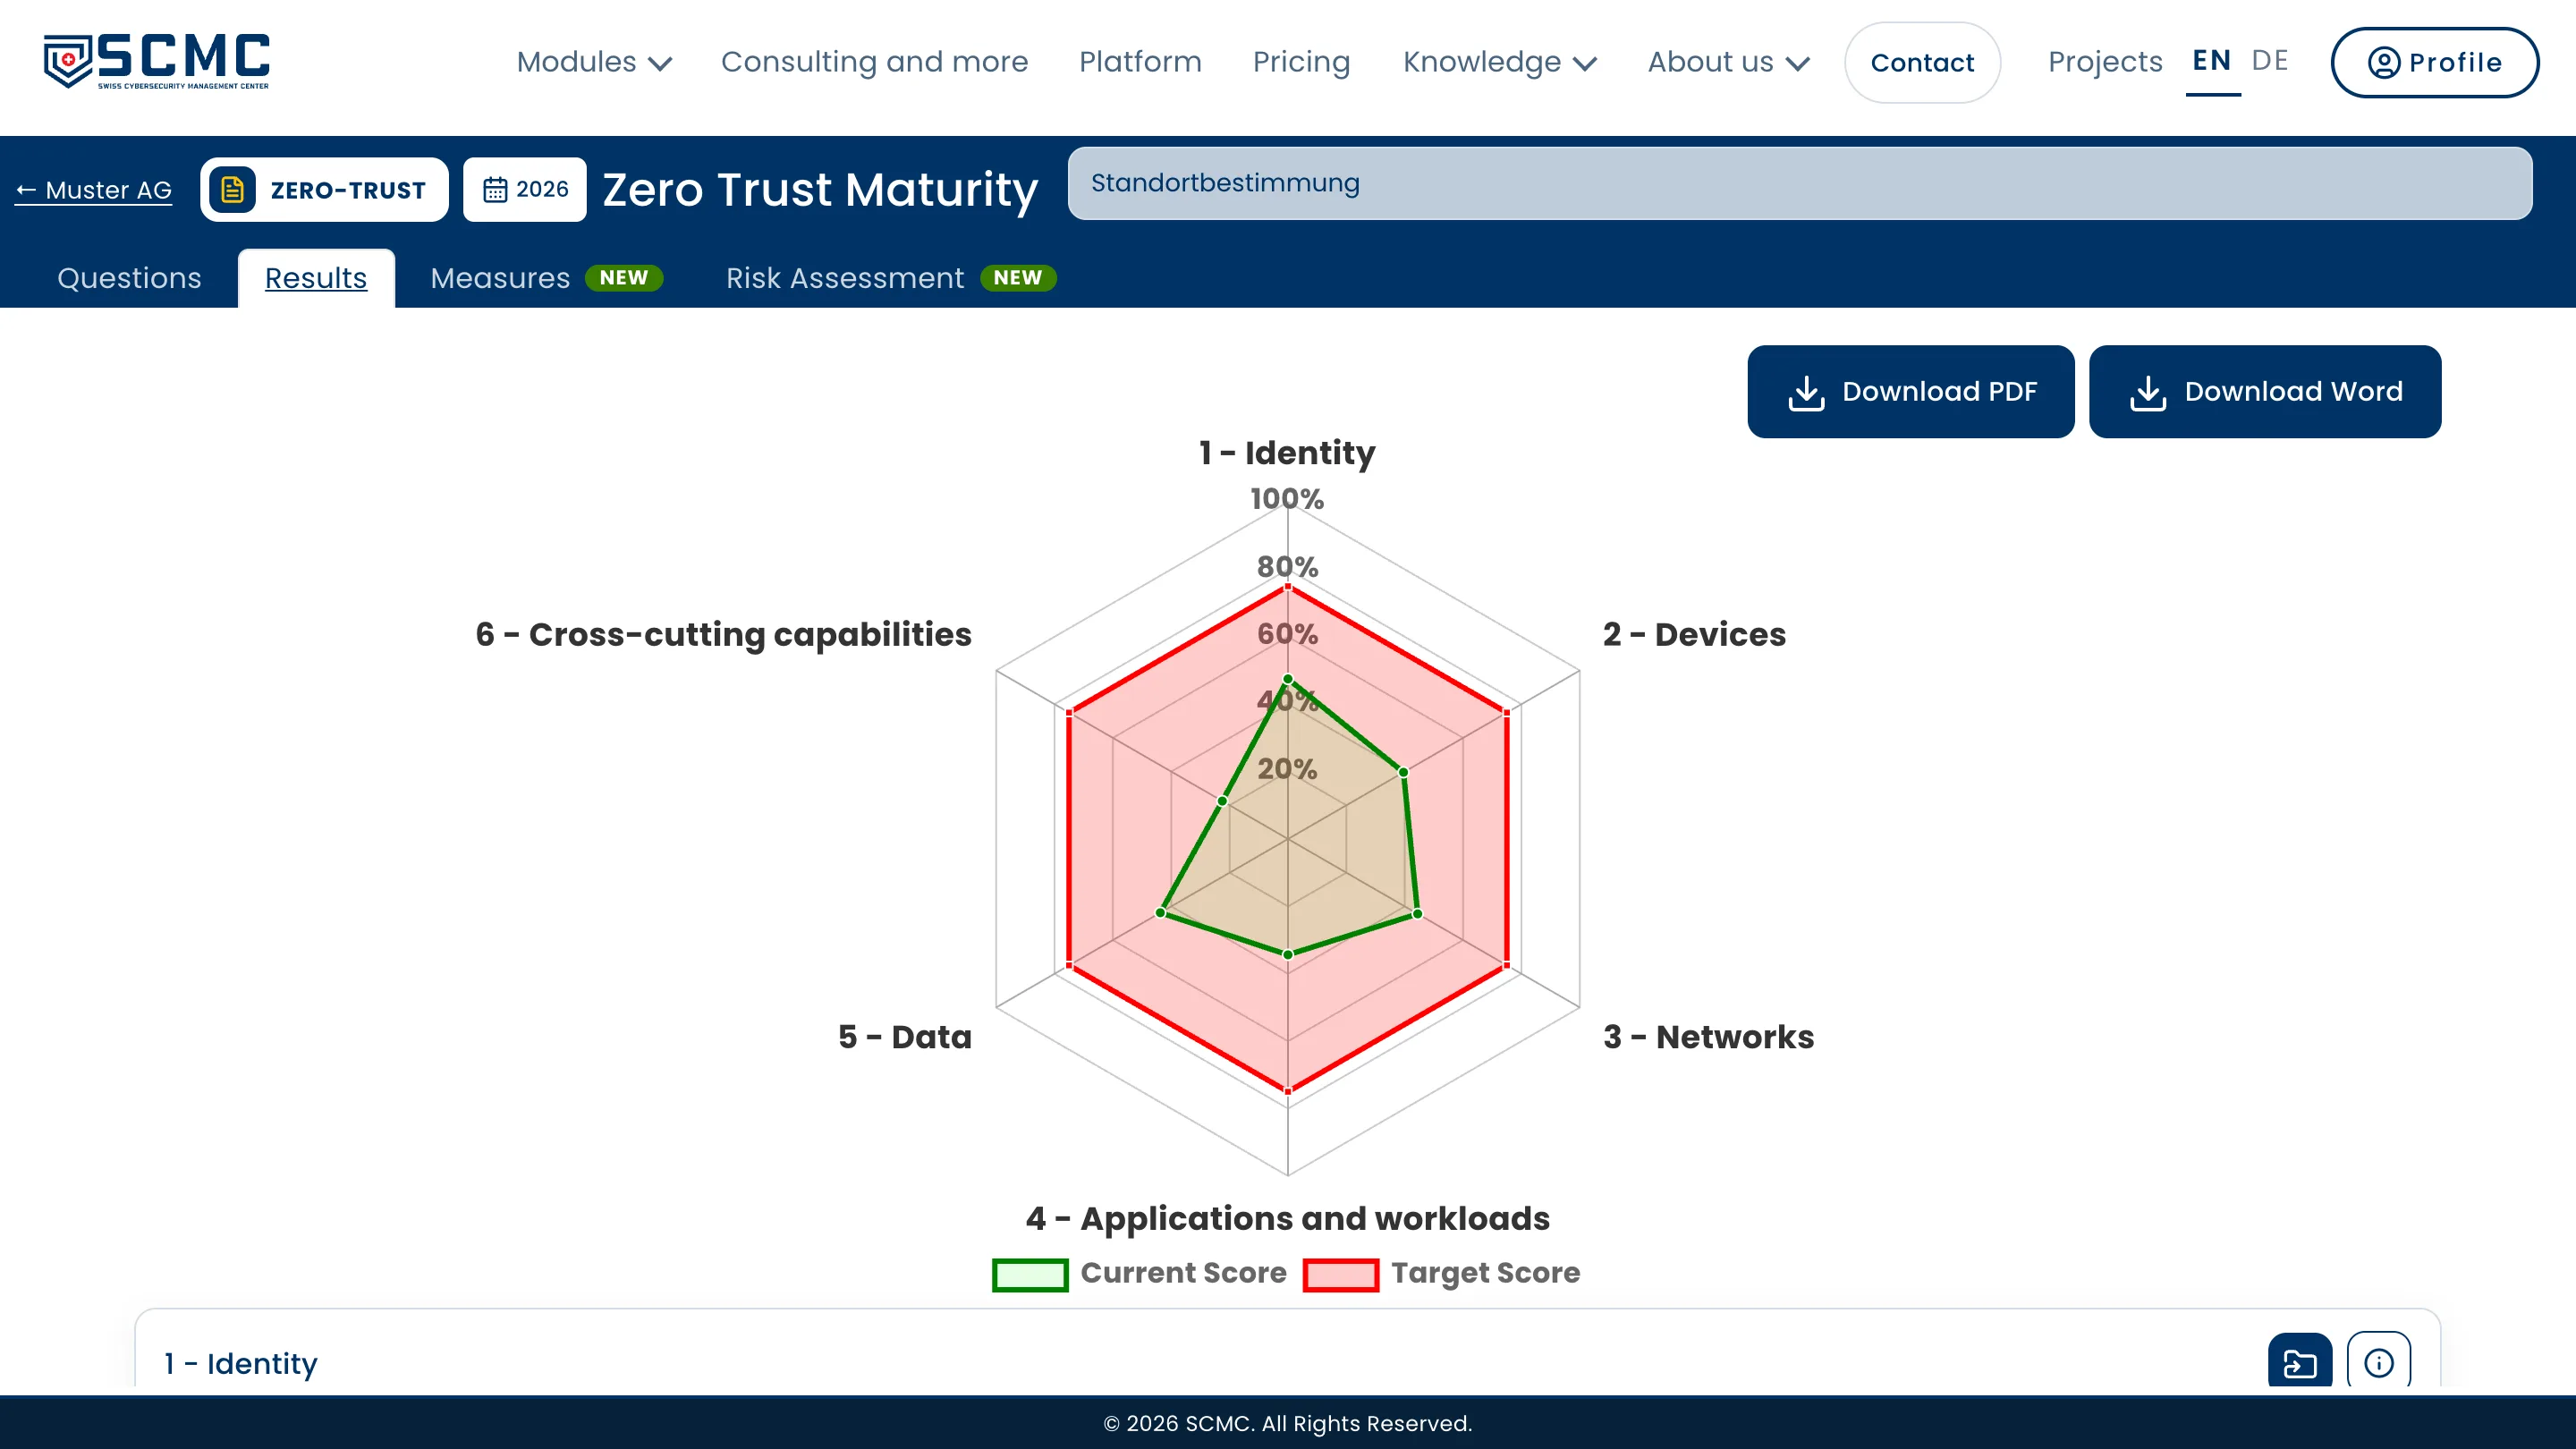
57 questions based on the Zero Trust Maturity Model of the US agency CISA, tailored to SMEs. You see your maturity per pillar, from sign-in to data.

Attacks rarely start at the firewall today. They start with a phished password, a neglected device or remote maintenance that is always open. Zero trust means that no access counts as safe just because it comes from the company network. The check shows where your company stands and draws on current cases of the Swiss police on cybercrimepolice.ch (in German), such as the attacks on networked refrigeration systems. To turn the result into a plan, add the Measures plan for CHF 850 a year. It brings measures and a risk assessment for every question.
All you need is an account. Zero Trust Maturity stays free, like the Basic Check.
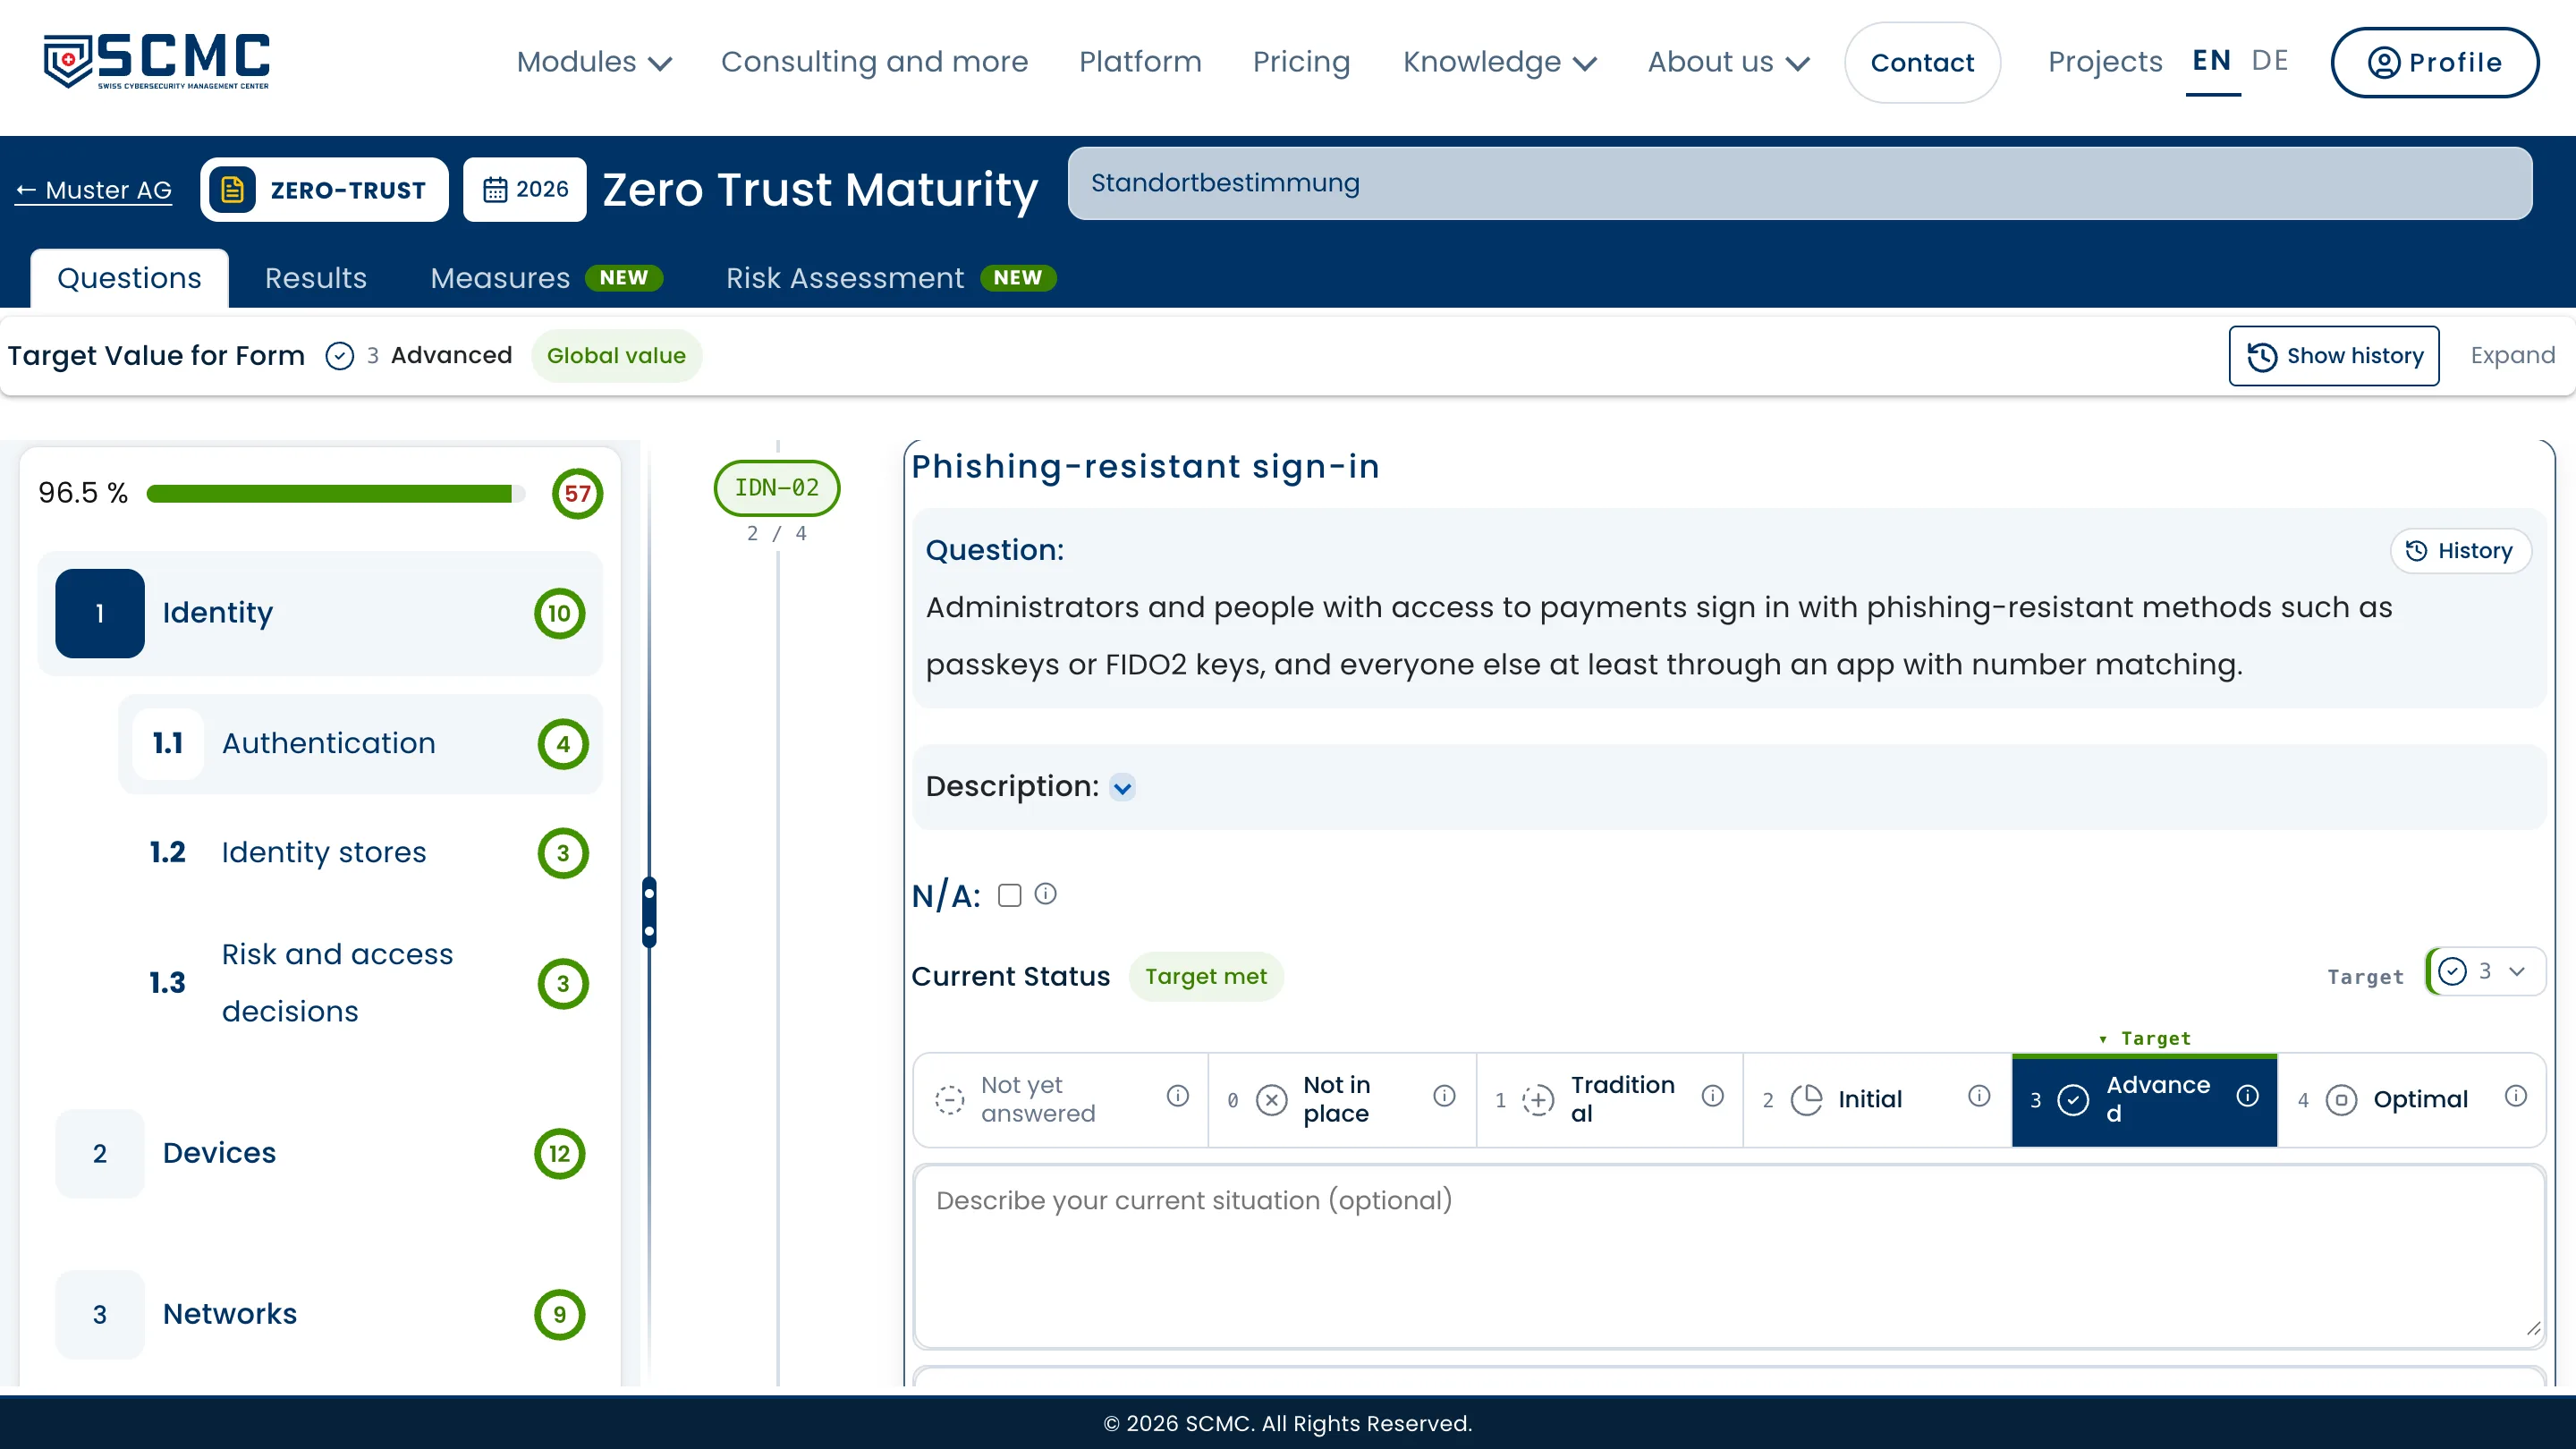
The questions are written for SMEs that run their IT with a service provider. Each question says what belongs to it at least and what the four levels look like.
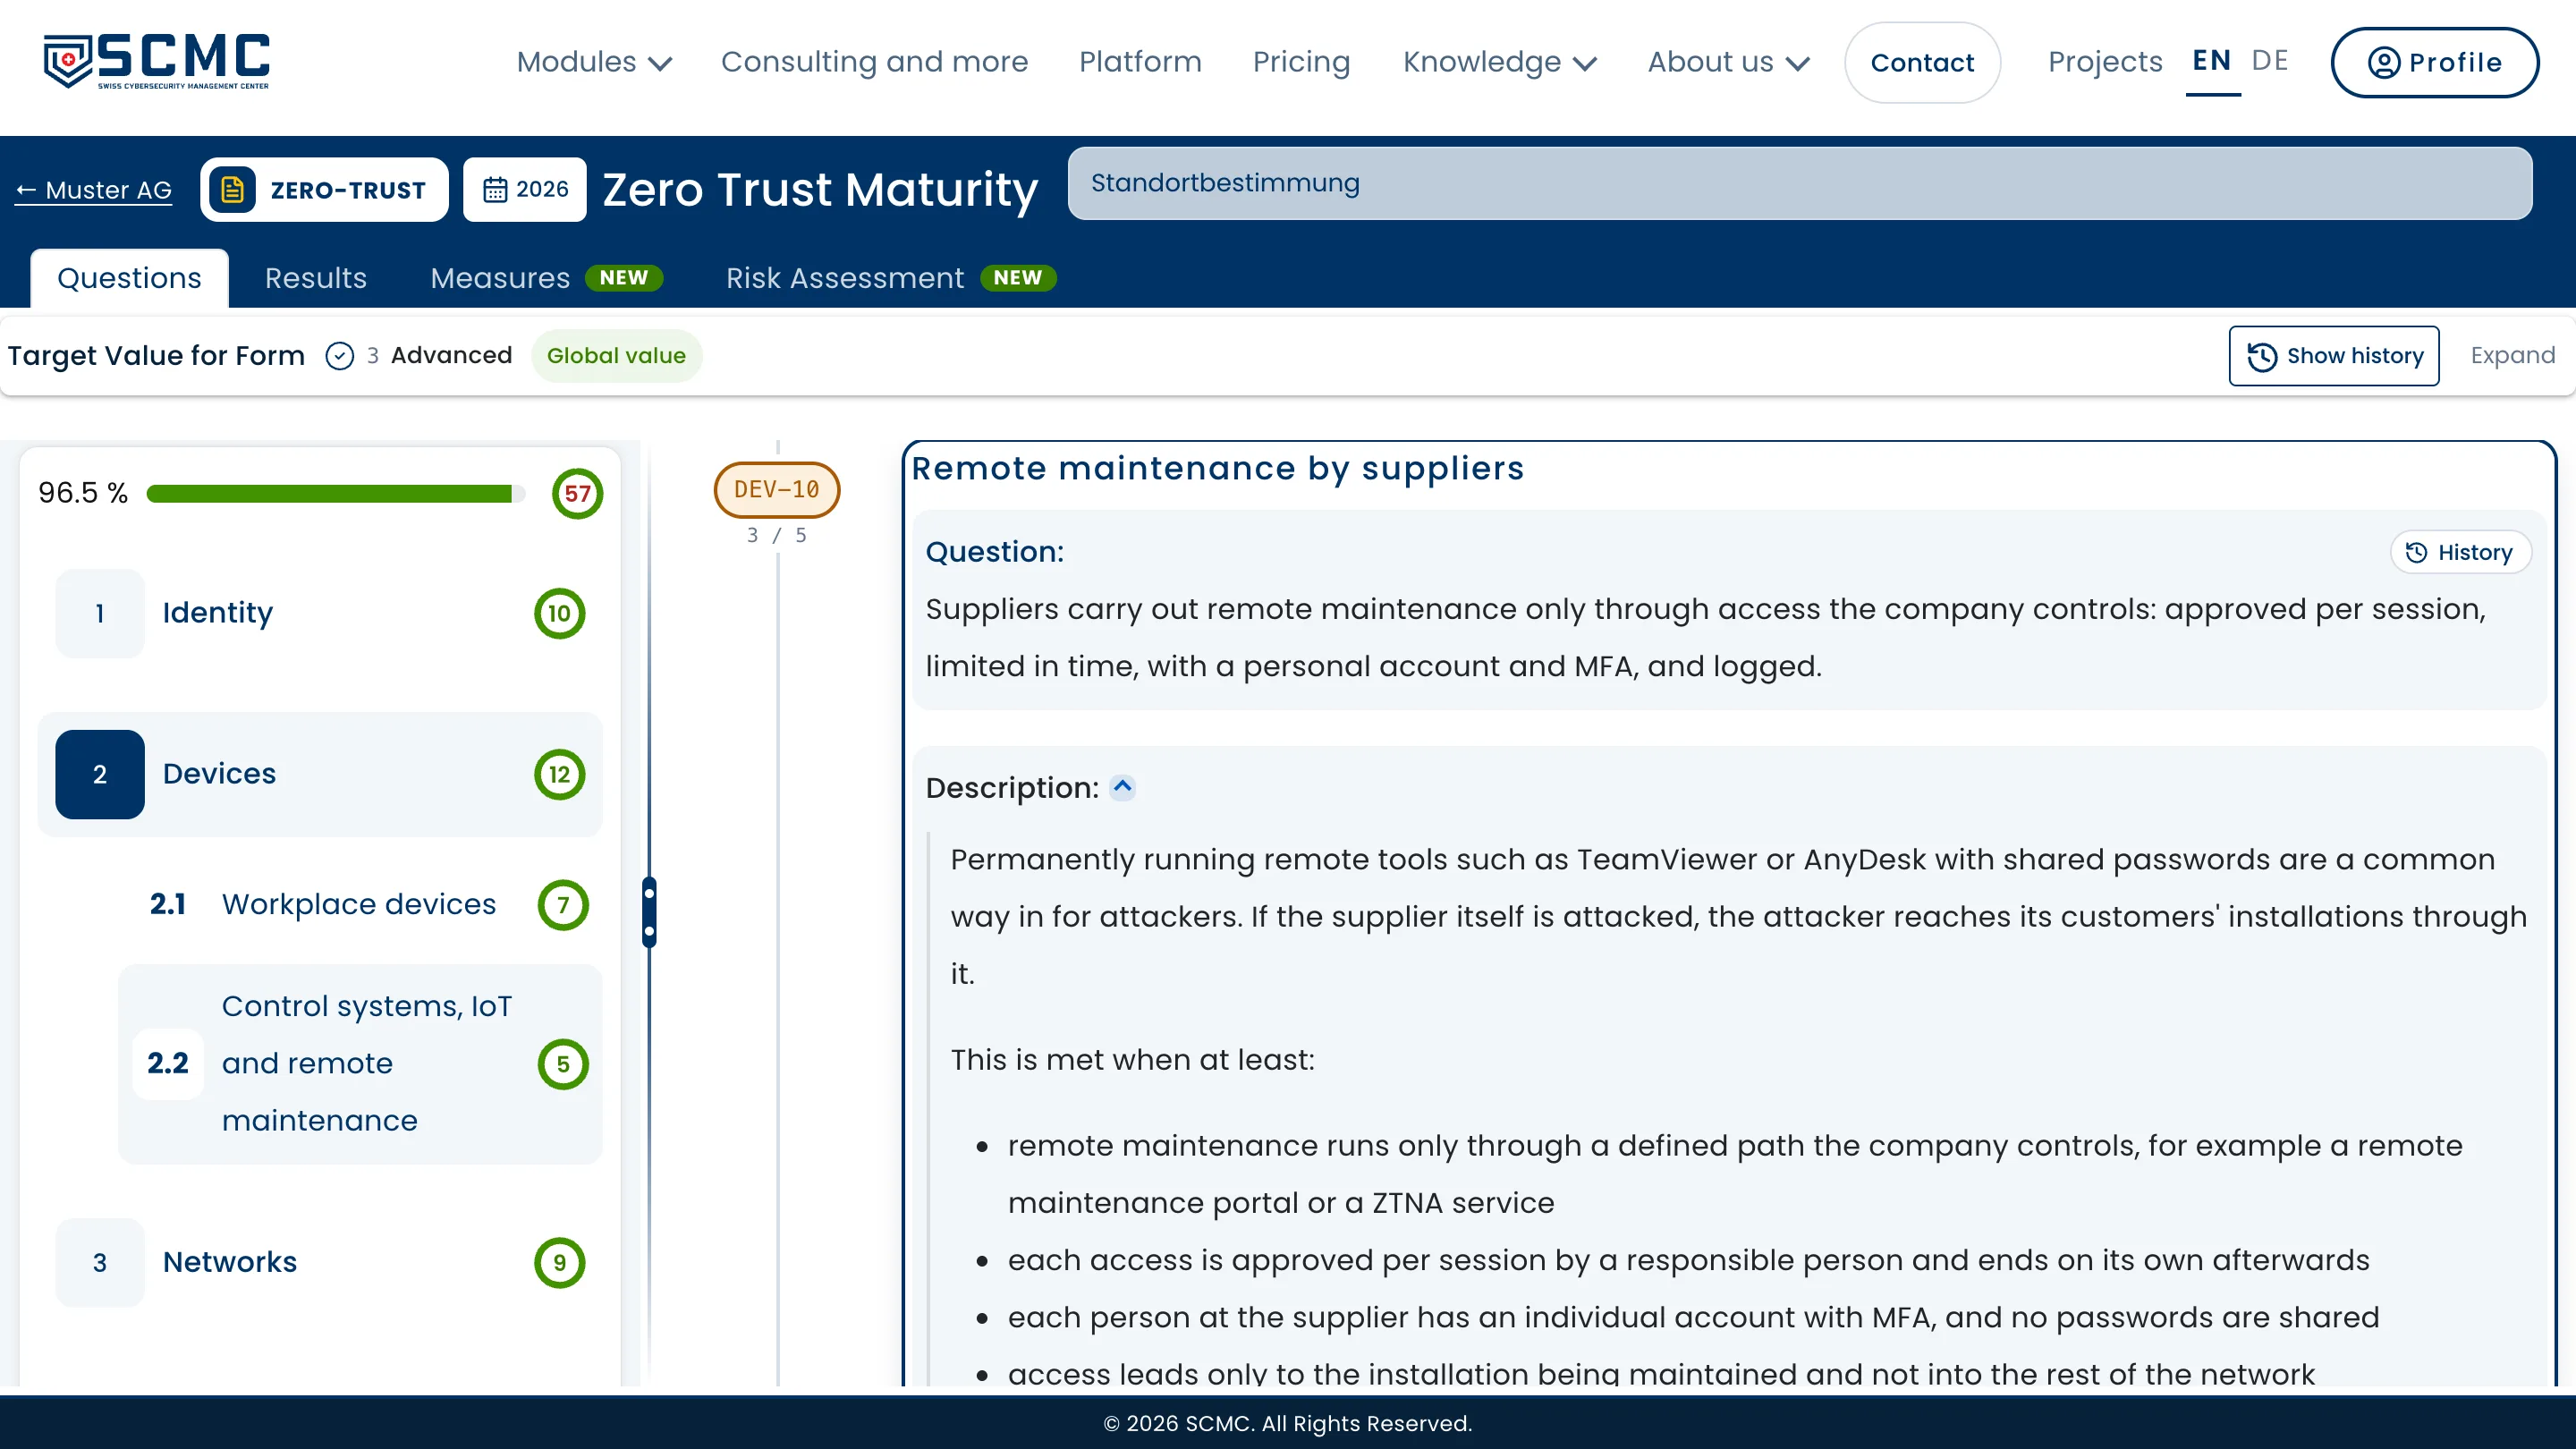
A separate part asks about refrigeration, heating, access control, cameras and remote maintenance by suppliers. Attackers start there more and more often.
Each question names the matching requirements of NIST CSF 2.0, the ICT Minimum Standard and ISO/IEC 27001. So for every answer you see which requirements of these frameworks it concerns.
Start for free. Or arrange a conversation if you have questions.
Swiss Made Software · Data stored exclusively in Switzerland
Yes. The assessment is free and needs no subscription. To turn the result into a plan, add the Measures plan for CHF 850 a year: measures and a risk assessment for every question. It applies to all free checks, the Basic Check included.
On the Zero Trust Maturity Model 2.0 of the US agency CISA with its five pillars identity, devices, networks, applications and data plus the cross-cutting capabilities. NIST SP 800-207 and the technology assessment of the Swiss Federal Office for Cyber Security (FOCS) complement it. Each question is mapped to NIST CSF 2.0, the ICT Minimum Standard and ISO/IEC 27001.
No. The questions describe in plain words what is meant, and each level has an explanation. Terms such as ZTNA or conditional access are explained in the description of the question.
No. Zero Trust Maturity is a self-assessment. SCMC reads no data from your systems and installs nothing. You answer the questions yourself or with your IT service provider.
You and the people you invite. At SCMC only one person in support can access a project, and every access is documented and logged. Data is stored exclusively in Switzerland.